Best developer security tools in 2026
Scanning, secrets, and supply chain tooling that fails loudly by design.
Security tooling is judged on two numbers that pull against each other: what it catches, and how often it is wrong. A scanner that flags everything gets muted within a week, which is the same as not having one. Almost none of that is measurable from a landing page, so watching this category early is mostly about learning how a tool expects to be tuned and who it expects to read the output.
6 tools · 1 launching soon
helpers.work
Launched17 free online tools for developers, DevOps and sysadmins
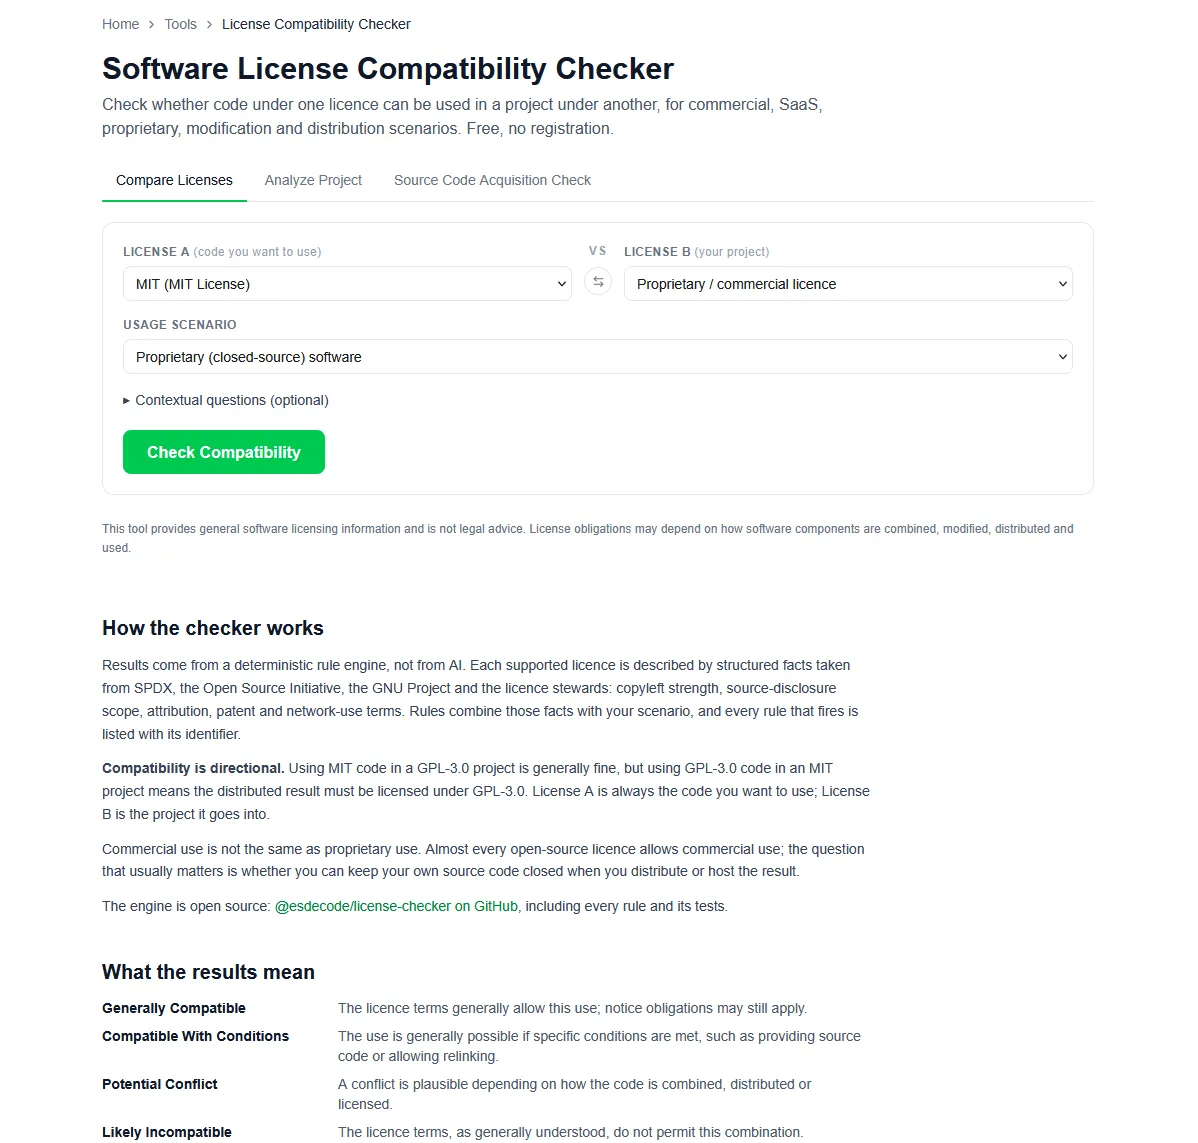
License Compatibility Checker
LaunchedCheck software license compatibility and identify potential conflicts before combining or distributing code.
Drop
LaunchedA rootless Linux sandbox for isolating coding agents and third-party programs.
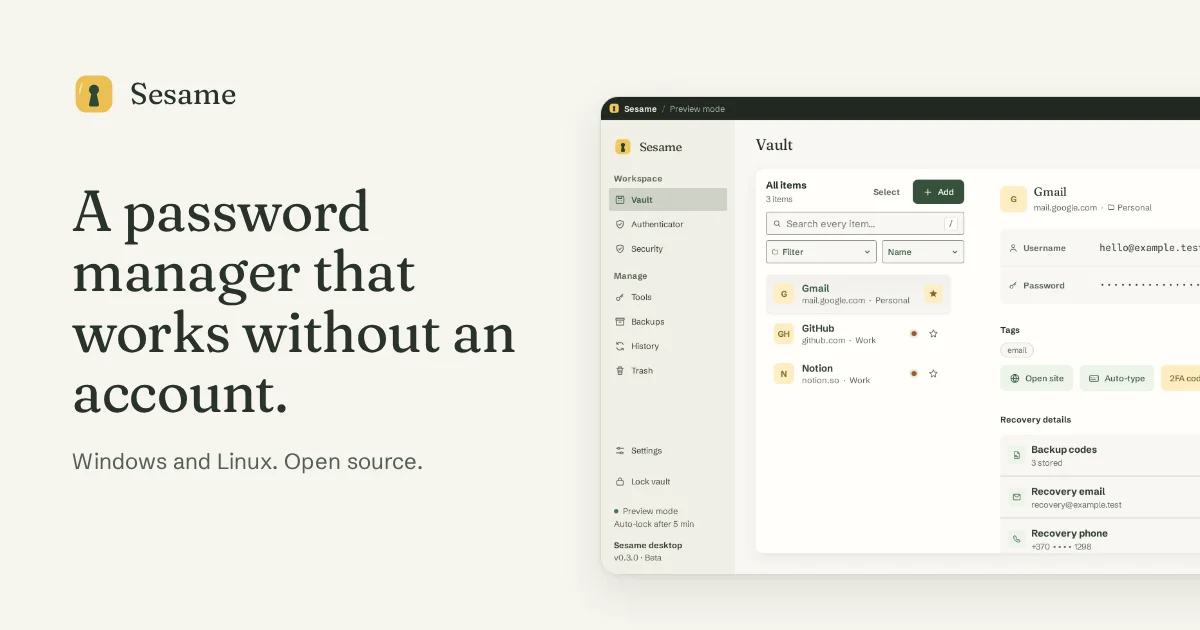
Sesame
BetaAn open-source password manager that works without an account, with your vault as a local file.
Clerk
LaunchedAuthentication and user management with prebuilt components for React and Next.js.
Launching soon
Upcoming Security tools
Listings with a launch still ahead of them. Join the waitlist now and the launch date lands in your inbox.
Evaluating
What to look for
Questions that are far easier to ask before a launch than after one.
Ask about false positives, not just coverage
Coverage lists are easy to publish. What matters is how a finding is suppressed, whether the suppression is reviewable, and how the tool behaves on a repository nobody has ever scanned.
Check where it runs and what it sends
A scanner that uploads your source or your logs is a new entry in your threat model. Local-first and hosted tools are different products behind the same pitch.
See whether it blocks or reports
A tool that fails the build changes how your team works; one that opens an issue does not. Both are defensible, and knowing which it is tells you who has to agree before you adopt it.
FAQ
Questions about this category
Are these tools audited or vetted by you?
No. Every listing is reviewed by a person for accuracy and quality, but that is editorial review, not a security assessment. Treat anything here as a candidate to evaluate, never as a recommendation.
What is worth asking a security tool before it launches?
How findings are suppressed, where the analysis runs, and whether it is designed to block a build or open an issue. Those three answers cover most of what adopting it would feel like.
Nearby
Related categories
Corners of the stack that overlap with this one, either in the listings themselves or in practice.
Open Source
Projects with public code, whether they are pre-1.0, pre-launch, or pre-announcement.
45 tools
Developer Tools
The wide bucket: CLIs, local environments, test runners, and code review.
60 tools
DevOps
CI, deploys, environments, and the tooling that keeps production boring.
15 tools
APIs
Gateways, SDK generators, mock servers, and contract testing.
12 tools